
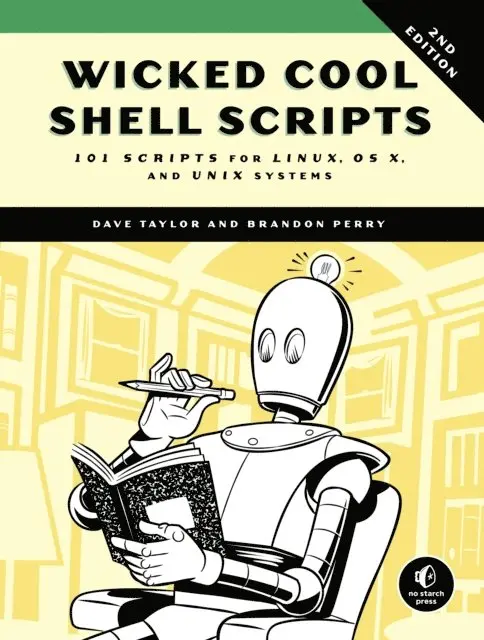
Gray Hat C#
Creating and Automating Security Tools
E-bok
Engelska, 2017454 kr
Läs direkt i Bokus Reader – eller ladda ned till din enhet
Fler format och utgåvor
Beskrivning
Learn to use C#''s powerful set of core libraries to automate tedious yet important tasks like performing vulnerability scans, malware analysis, and incident response. With some help from Mono, you can write your own practical security tools that will run on Mac, Linux, and even mobile devices.
Following a crash course in C# and some of its advanced features, you’ll learn how to:
-Write fuzzers that use the HTTP and XML libraries to scan for SQL and XSS injection
-Generate shellcode in Metasploit to create cross-platform and cross-architecture payloads
-Automate Nessus, OpenVAS, and sqlmap to scan for vulnerabilities and exploit SQL injections
-Write a .NET decompiler for Mac and Linux
-Parse and read offline registry hives to dump system information
-Automate the security tools Arachni and Metasploit using their MSGPACK RPCs
Streamline and simplify your work day with Gray Hat C# and C#’s extensive repertoire of powerful tools and libraries.
Following a crash course in C# and some of its advanced features, you’ll learn how to:
-Write fuzzers that use the HTTP and XML libraries to scan for SQL and XSS injection
-Generate shellcode in Metasploit to create cross-platform and cross-architecture payloads
-Automate Nessus, OpenVAS, and sqlmap to scan for vulnerabilities and exploit SQL injections
-Write a .NET decompiler for Mac and Linux
-Parse and read offline registry hives to dump system information
-Automate the security tools Arachni and Metasploit using their MSGPACK RPCs
Streamline and simplify your work day with Gray Hat C# and C#’s extensive repertoire of powerful tools and libraries.
Produktinformation
Utforska kategorier
Hoppa över listan
Du kanske också är intresserad av
- 10% rabatt på allt
- 10% rabatt på allt
- 10% rabatt på allt
Del 11
- -19%
- 10% rabatt på allt
- Signerad!
Del 3
- 10% rabatt på allt
Del 4
- 10% rabatt på allt